Endpoint Telemetry and Investigation
A controlled encoded PowerShell execution on a Windows endpoint raised a level-12 Wazuh alert. I traced it from the Sysmon process event to the central alert, decoded what it ran, tested a detection query against a baseline (unencoded) comparison, and closed it as authorized activity.
At a Glance
- Scenario
- Encoded PowerShell execution on a Windows endpoint
- Environment
- Azure · Windows 11 · Sysmon · Wazuh 4.14.8
- Question
- What ran, and was it authorized?
- Decision
- Closed as authorized lab activity; concern Low
- Skills
- Sysmon · Wazuh · PowerShell · Python
01Environment
- PowerShell executionclient01\clientadmin
- Sysmon Operational channelEvent ID 1
- Wazuh agentID 001
- Private VNet peeringno public path
- Wazuh managerexisting rules
- Alert JSONstored alerts
Collection was verified end to end: both executions appear in local Sysmon and in Wazuh.
02Controlled Test
Two runs of the same harmless operation, from the same account and PowerShell parent. The marker file was reset between them.
| Execution | Invocation | Result |
|---|---|---|
| Positive | -EncodedCommand <UTF-16LE Base64> | Exit code 0; marker verified |
| Comparison | Same operation with -Command | Exit code 0; marker verified after reset |
The 216-character Base64 argument recorded by Sysmon decoded (UTF-16LE) to a single command that writes a marker file to the user's temp folder:
Set-Content -Path (Join-Path $env:TEMP 'ct-case2-marker.txt') -Value 'CT-P2-TEST'03Timeline
October 20, 2026. All times UTC.
- 1Encoded run
07:28:10.051. The encoded command started as
client01\clientadmin. - 2Sysmon Record 7960
07:28:10.812. Process creation for
powershell.exe, child PID 10012. - 3Alert: level 12
07:28:11.892. Existing Wazuh rule 92057 fired about a second later.
- 4Marker verified
Exit code 0, and the file held
CT-P2-TEST. - 5Baseline run
08:12:08.866. The same operation with
-Command, after a marker reset. - 6Sysmon Record 8016
08:12:08.890. Process creation, child PID 1052.
- 7Alert: level 4
08:12:09.940. Existing Wazuh rule 92027.
- 8Query and decision
MATCH on 7960, NON-MATCH on 8016. Closed as authorized.
04Correlation
Local Sysmon records matched to their Wazuh alerts, using the retained Sysmon XML and alert JSON.
| Field | Encoded run | Baseline run |
|---|---|---|
| EventRecordID | 7960 | 8016 |
| Child PID | 10012 | 1052 |
| Parent process / PID | powershell.exe / 1388 | powershell.exe / 1388 |
| Account | client01\clientadmin | client01\clientadmin |
| Wazuh rule / level | 92057 / 12 | 92027 / 4 |
| Query result | Match | Non-match |
Eight selected field checks passed for each event pair, including the ProcessGuid.
05Detection Logic
A manual Python query over the stored Wazuh alerts. It flags an execution characteristic, not malicious intent: encoding is also used in legitimate automation.
import re

def matches(record):
    win = record.get("data", {}).get("win", {})
    system = win.get("system", {})
    event = win.get("eventdata", {})

    command = event.get("commandLine") or ""
    image = event.get("image") or ""

    return (
        str(record.get("agent", {}).get("id")).zfill(3) == "001"
        and str(system.get("eventID")) == "1"
        and system.get("providerName") == "Microsoft-Windows-Sysmon"
        and image.lower().endswith("\\powershell.exe")
        and re.search(
            r"(?<!\S)-EncodedCommand(?=\s|$)",
            command,
            re.IGNORECASE
        ) is not None
)- Record 7960 · encoded runMATCH
- Record 8016 · baseline runNON-MATCH
Wazuh's existing rules fired on their own; the query was never deployed as a rule. The baseline run still reached Wazuh, so its NON-MATCH came from the query condition itself.
06Decision
- No PowerShell Event ID 4104 record was correlated; the command came from decoding the Base64 captured by Sysmon.
- The marker check came from the test's own output, not a correlated file-creation event.
- Other activity on the endpoint was not reviewed in full.
- The query was tested on one encoded and one baseline run, so it gives no accuracy or false-positive rate.
- The central records were stored Wazuh alerts, not a raw-event archive.
07Evidence
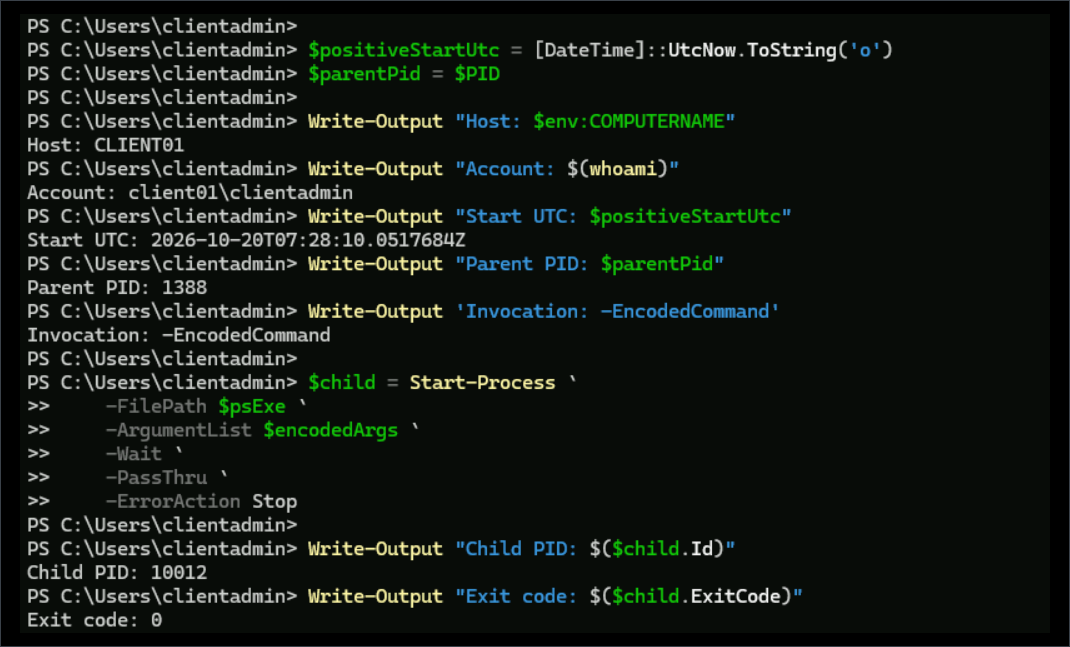 Screenshot 01Encoded PowerShell execution
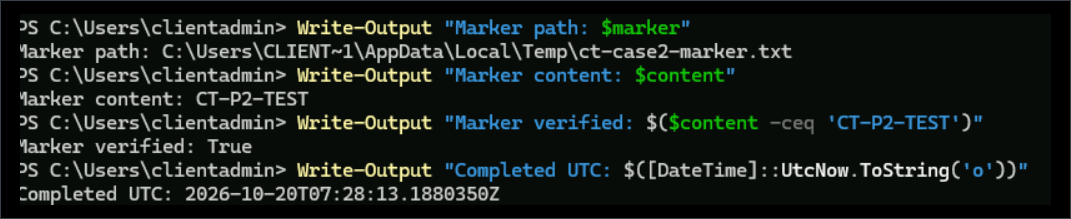 Screenshot 02Marker content verified
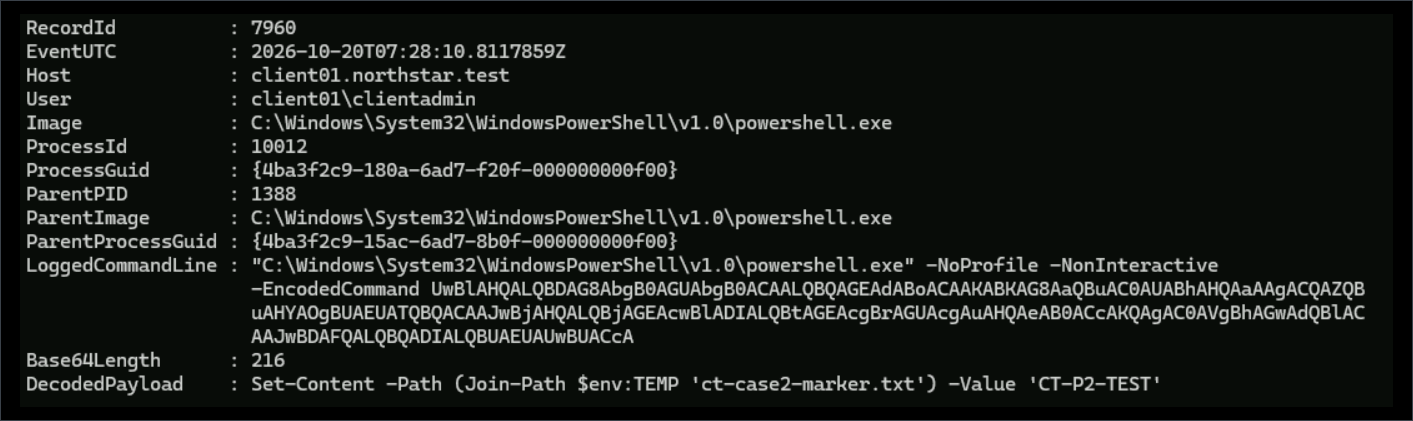 Screenshot 03Local Sysmon event, Record 7960
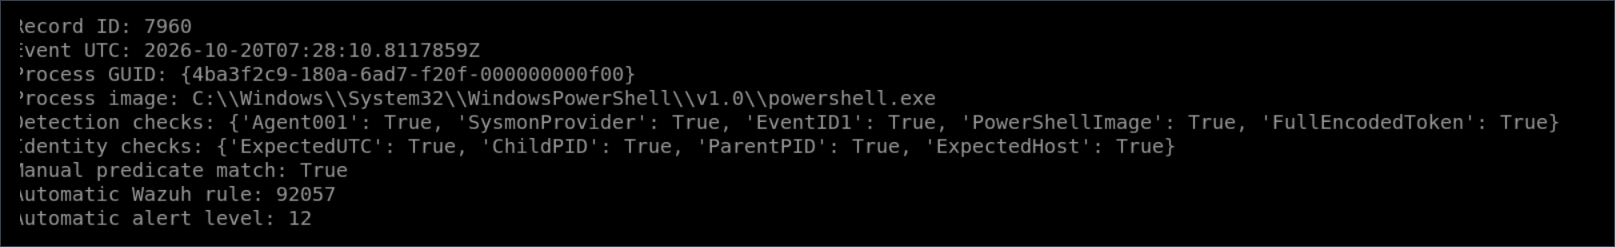 Screenshot 04Query MATCH on Record 7960
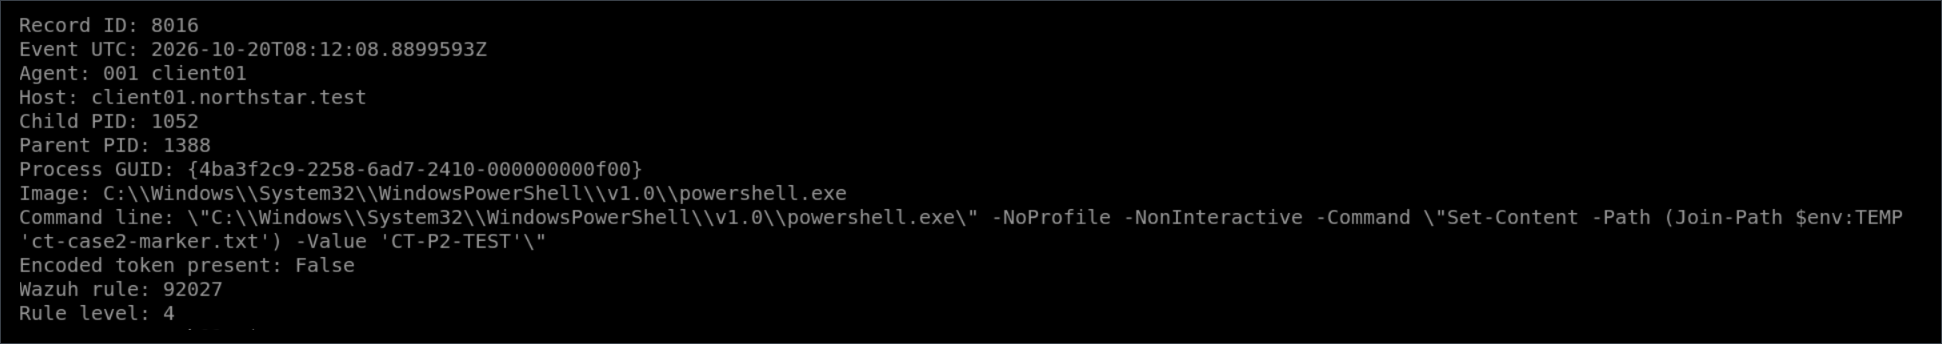 Screenshot 05Central Wazuh record, Record 8016
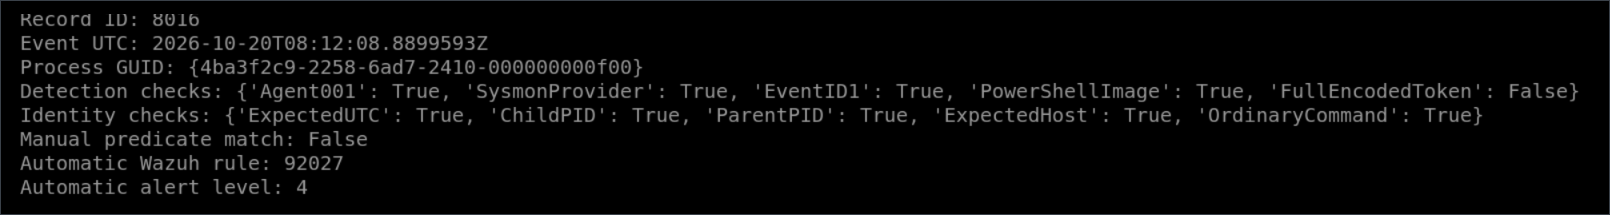 Screenshot 06Query NON-MATCH on Record 8016